

MCP Server Development Services
When AI needs to open a ticket, look up an order, or draft an update in your CMS, those actions should run through tools your security team can scope, log, and revoke.
We build Model Context Protocol servers that wrap the APIs and data you already own, so assistants get reliable capabilities without a one-off integration for every new model.
We start with a narrow set of high-value tools, then expand once permissions, observability, and human review prove the pattern is safe to grow.
MCP and AI Tool Programs
What an MCP Server Lets AI Do for Your Business
Look up live records
Draft updates for review
Run scoped actions
Tool Contracts, Permissions, and Operations
Use case and policy
Tool contracts
Implement and observe
Where MCP Sits in Your AI Stack
AI agent orchestration
RAG development
API and integration layer
You can count on us.
Firm Price
The price we quote for a scope of work is the price you pay. No surprises.
Detailed Plan
Visual and written plans make clear the scope of work and guide the project to success.
Steady Cadence
Progress and working decisions arrive on an agreed, dependable rhythm.
Prompt Communication
Questions and issues are acknowledged promptly, with clear ownership and next steps.
Frequently Asked Questions
What is an MCP server?
A Model Context Protocol (MCP) server exposes scoped tools and data to AI assistants through a standard contract. Instead of custom glue for every assistant, your team defines which actions are allowed, how they authenticate, and what gets logged when a model calls a tool.
How is MCP different from an API?
Your business APIs stay the source of truth. MCP sits in front of them with tool definitions, examples, and guardrails tuned for model use. Assistants discover capabilities consistently, and operators can version or retire tools without rewriting every integration.
Which systems can it connect?
Any system you can reach with a supported API or database connection: CRM, commerce, ticketing, CMS, email, Slack or Teams, ERP, and internal databases. We narrow initial tools to high-value, low-risk actions, then expand once telemetry shows safe behavior.
How do sign-in and permissions work?
Tools run under service accounts or per-user OAuth, depending on policy. Each session carries scopes that limit which records or actions are available, and structured logs capture who invoked which tool with what result. Sensitive actions can require confirmation or human approval in your application layer.
Can we move existing integrations to MCP?
Often yes. If you already have REST or GraphQL services, we can wrap them as MCP tools with clearer schemas and centralized auth. The goal is not to replace working APIs, but to give assistants one governed surface instead of ad hoc scripts per use case.
How do we start?
Share the systems, policies, and allowed actions you want assistants to perform. We map one or two tools against staging data, prove logging and permissions, then harden for production and expand the toolkit with your security and operations teams involved.
The People Leading Your Work
 Gabriel RichardsFounder and CEOSince 2000
 Roberto OlmosChief Technology OfficerSince 2004
 Cheyne PhillipsChief Operating OfficerSince 2014
 Jonathan AndersonChief Solutions OfficerSince 2017
Guides from Our Engineers
We Run Our Agency on MCP
 Gabriel Richards

Building an AI Support Workflow with a Remote MCP Server: A Production Case Study
Gabriel Richards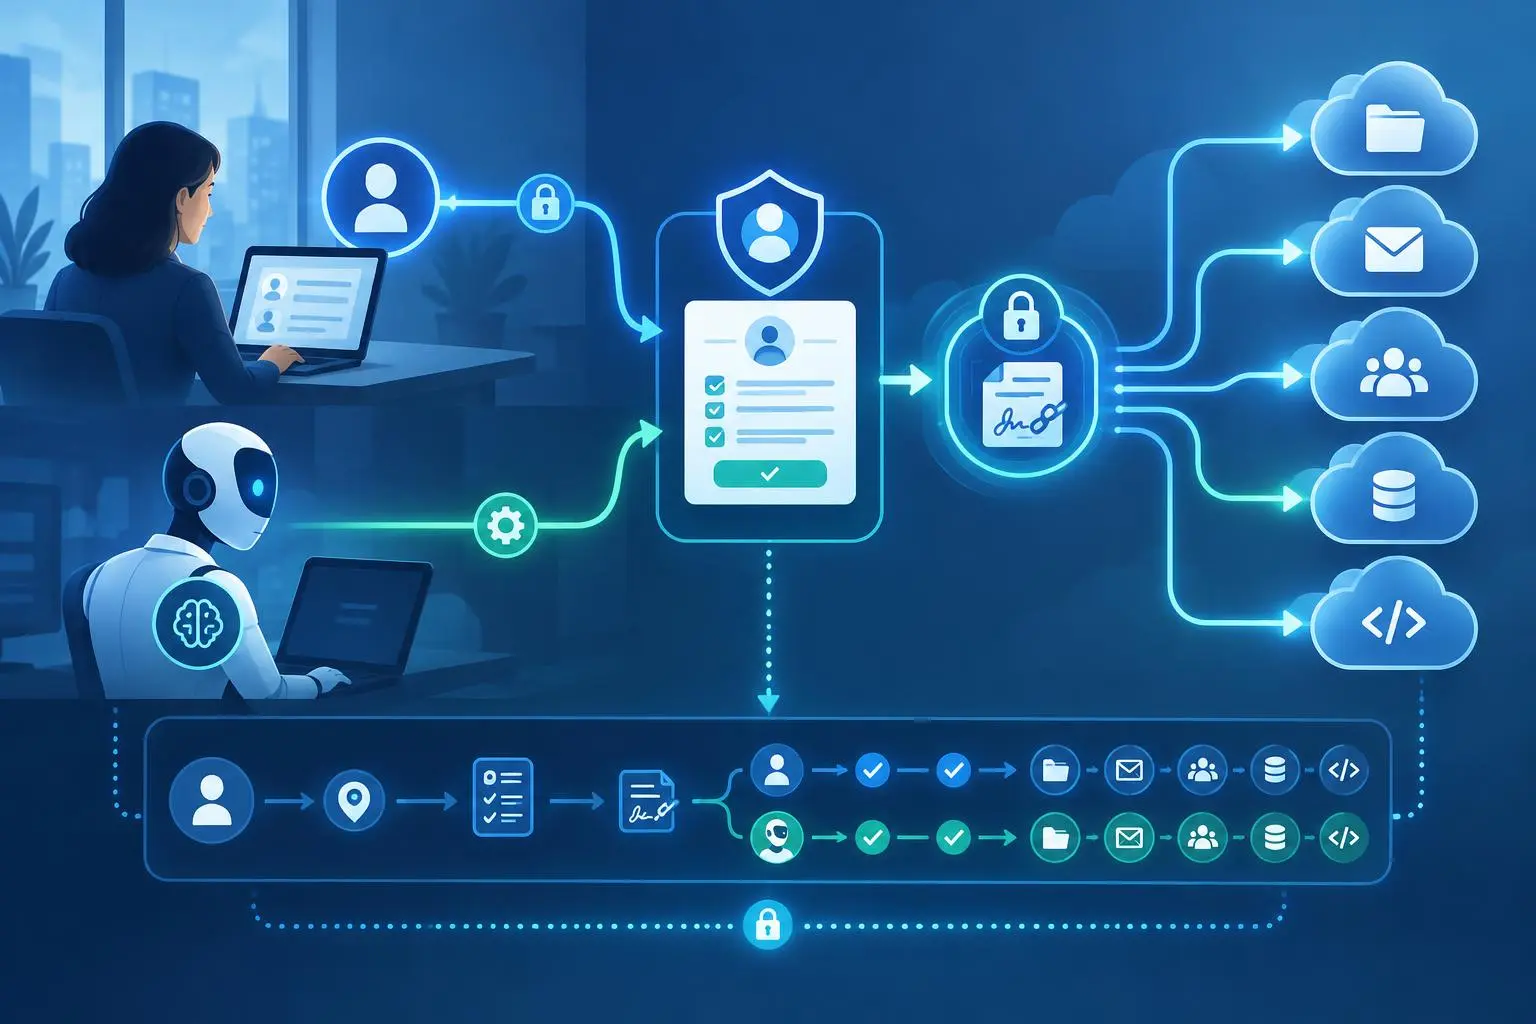
Giving AI Agents Real Employee Identity With MCP OAuth
Gabriel Richards
Endertech MCP 101 Webinar - How does MCP relate to ChatGPT, Claude, Grok, etc...
Gabriel Richards
Prompt-Based Product Discovery Demo Using MCP
Gabriel Richards

- 4.9 / 534 Clutch reviews
- Since 2000experience that compounds
- 300+clients served